OpenRMF® Professional
Keep your ATO package current without rebuilding it by hand.
SimIS is an authorized value added reseller of OpenRMF® Professional from Soteria Software. We deploy it inside your boundary and support your team after go-live.
Start an evaluationWhat It Does
Your scans already hold most of what an ATO package needs. The work is turning thousands of SCAP results, checklist files, and patch scans into a POA&M and a compliance picture an authorizing official will accept, then doing it again every quarter when DISA updates the STIGs. OpenRMF® Professional reads that data directly and keeps it connected, so a new scan updates the package instead of starting another spreadsheet.
Live POA&M
Findings flow into the POA&M as scans and checklists change, with no re-entry.
Read moreChecklist Management
Every DISA, CIS, and custom checklist in one place, upgraded in bulk.
Read moreInventory and PPSM From Scans
Hardware, software, and ports/protocols/services lists that build themselves.
Read moreCompliance Generation
RMF, FedRAMP, CMMC, or a custom framework, down to the sub-control and CCI.
Read moreBuilt to Run Inside Your Boundary
OpenRMF® Professional is installed software rather than a hosted service. It runs on-premise, on an air-gapped network, on a VM or Kubernetes, or in your own cloud tenant, and Soteria reports that more than half of its customers and evaluators run it disconnected. Login supports CAC/PIV and Active Directory. It holds Navy DADMS ID #141351, and licensing counts installations and active system packages, with unlimited users.
Works With What You Already Run
OpenRMF® Professional doesn't scan, and it doesn't replace eMASS. It sits between them. SCC, Evaluate-STIG, and ACAS output comes in, and clean checklists and POA&M exports go out to your system of record. Findings can open tasks in Jira, ServiceNow, GitLab, or GitHub, and an open API lets you automate uploads from your own pipelines.
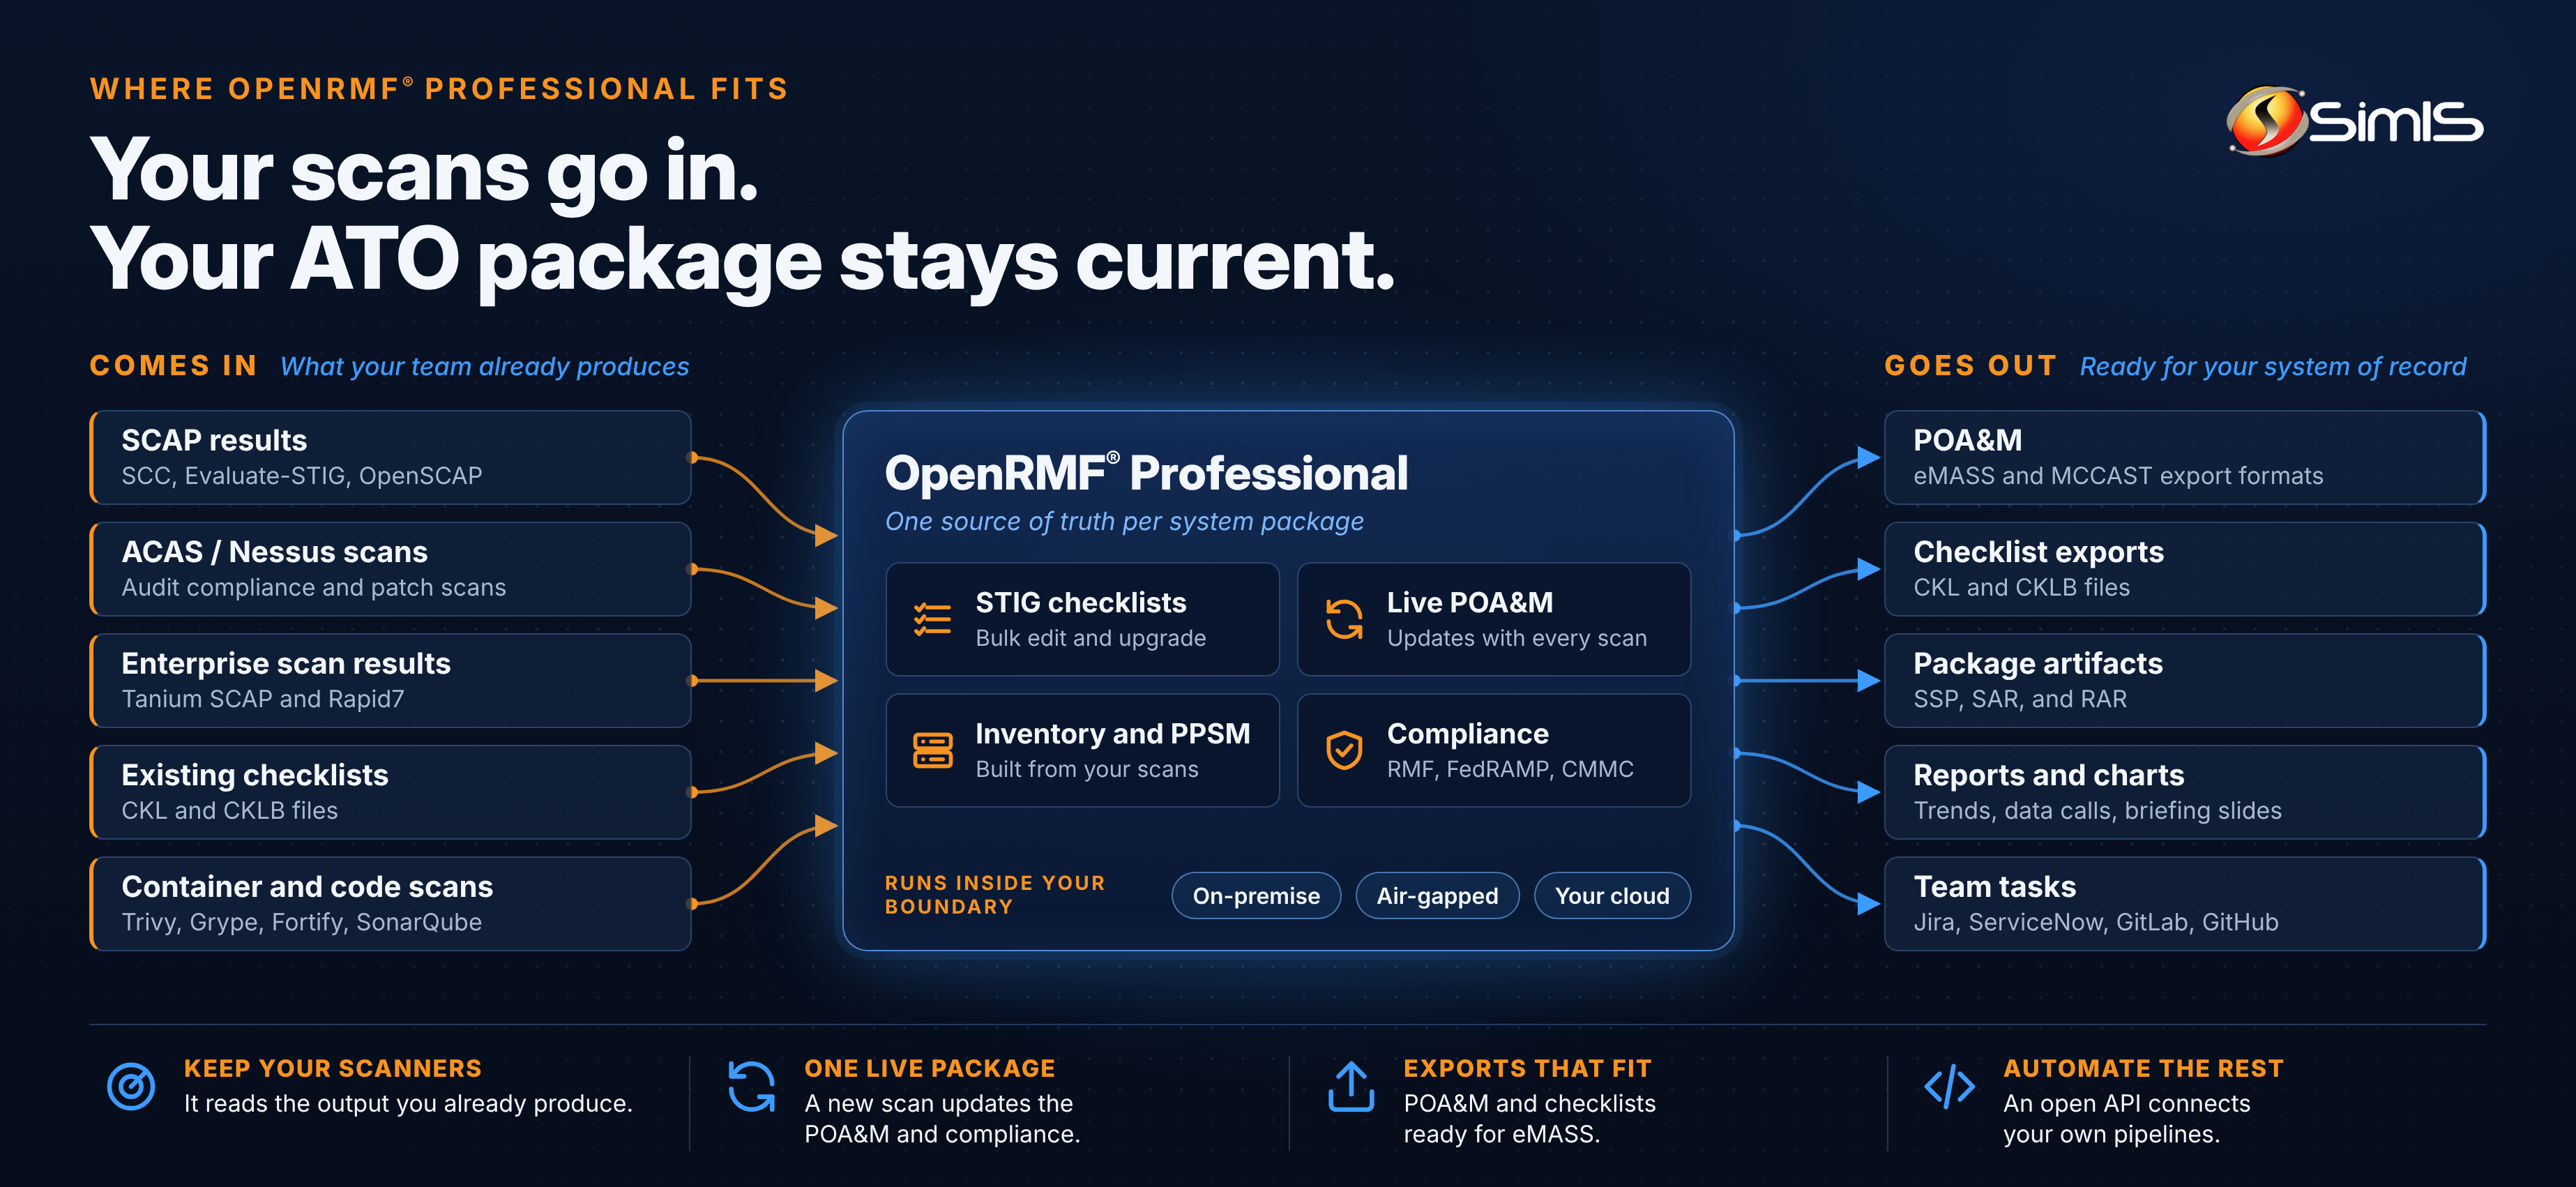
Nothing on the left changes. Your team keeps running the scanners it runs today, and the artifacts on the right go to the same system of record they go to now. What changes is the middle. Each new scan updates the checklists and the POA&M on its own, and current compliance is a click away.
If you run Elastic, OpenRMF® Professional connects to it through two service provider interfaces that come with your license. The Elastic AI interface syncs your compliance data, including the full text of your documents, into Elastic so your team can query it alongside operational logs and build rules and cases around it. The Elastic Security interface uses machine learning anomaly jobs to spot changes across your devices and update the affected accreditation packages automatically. Soteria's continuous ATO white paper walks through how the two work together.
For Primes Tracking Their Supply Chain
Primes can use OpenRMF® Professional to track CMMC, NIST SP 800-171, and RMF compliance across subcontractors in one structure, without opening their own networks to those subcontractors. Subcontractors keep a single record they can share across contracts. Soteria's prime contractor white paper covers the approach in more detail. SimIS also runs a CMMC compliance practice, so the people configuring your framework know how an assessor will read it.
What SimIS Brings
Evaluation
We stand up Soteria's 30-day full evaluation on your own scans, so the trial answers your questions instead of a scripted demo's. If you buy, the evaluation install carries straight into production.
Installation and migration
We install alongside your IT team and bring in your existing checklists, scans, and POA&M.
Training
We train your analysts and administrators, supplemented by Soteria's video courses.
Support
SimIS handles first- and second-line support directly, and Soteria's engineers handle anything that needs a product fix.
Buying
Purchase through SimIS, a Veteran-Owned Small Business. Our credentials are in our Trust Center.
See It Before You Talk to Anyone
- Live read-only demo
- Case study, a two-person Navy cyber team
- Case study, a Navy enterprise with 50+ ATOs
- Product data sheet
- Team Subpackages data sheet
- White paper, prime contractor supply chain compliance
- White paper, continuous ATO with Elastic
- Savings calculator
OpenRMF® is a registered trademark of Soteria Software LLC.
Live POA&M
Findings flow into the POA&M as scans and checklists change, with no re-entry.
Entries are created and updated from your latest scans, checklist edits, compliance statements, and inherited controls, with traceability in both directions. Mitigations and milestones live with each entry. When it's time to submit, export in the format your system of record expects, including eMASS and MCCAST.
Checklist Management
Every DISA, CIS, and custom checklist in one place, upgraded in bulk.
Import SCAP results from SCC, Evaluate-STIG, ACAS/Nessus, OpenSCAP, Rapid7, and Tanium, along with CKL and CKLB files. Bulk edit, lock, and upgrade across a whole package. Templates carry your standard answers forward, and every change is kept in history. Soteria packages DISA's quarterly releases into product updates, so upgrades don't mean copying answers by hand.
Inventory and PPSM From Scans
Hardware, software, and ports/protocols/services lists that build themselves.
Hardware and software inventories and your PPSM listing are pulled from the patch and compliance scans you already run. Add what can't be scanned and mark boundary crossings. Patch vulnerability trends are tracked over time, and container and code scan results from tools like Trivy, Grype, Fortify, and SonarQube sit in the same package.
Compliance Generation
RMF, FedRAMP, CMMC, or a custom framework, down to the sub-control and CCI.
Apply tailoring, overlays, and inherited controls, then generate compliance from the actual checklist and scan data. Track trends by control family and produce SSP, SAR, and RAR artifacts. Evidence attaches directly to packages, POA&M entries, checklist items, and compliance statements.
Reach Out
Not sure whether your packages are big enough to need this? Ask us. We'll tell you straight, and if it fits, we'll set up an evaluation on your own data.